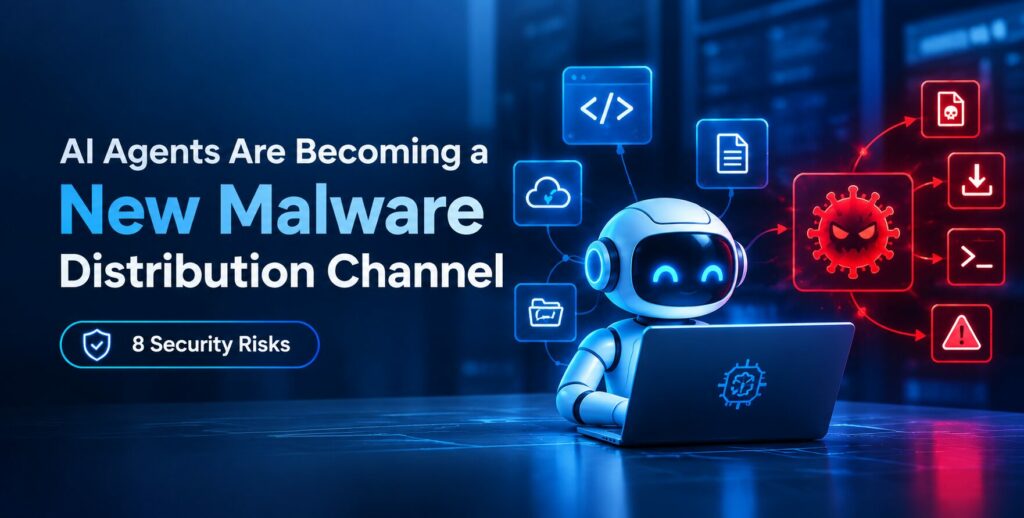
AI Agents Are Becoming a New Malware Distribution Channel
TL;DR
• AI agents can become targets for malware distribution.
• Fake repositories can manipulate AI recommendations.
• Tool poisoning can hide malicious instructions.
• Prompt injection can influence agent behavior.
• Malicious updates can turn trusted tools into threats.
• AI coding agents can create new execution risks.
• Strong permissions and monitoring can reduce exposure.
• Human approval remains important for sensitive actions.
AI agents are moving beyond simple chat and search. They can now browse websites, read documentation, use software tools, access repositories, execute code, and interact with external systems. As these capabilities expand, cybersecurity risks are also changing. For organizations following the growth of AI and autonomous systems, the issue is becoming increasingly important. AI Tech Updates
A recent report highlighted how attackers can exploit the trust that people and AI assistants place in software repositories, AI skills, connectors, and tool descriptions. Artificial Intelligence News reported on the FakeGit campaign and the growing risk of malicious software being discovered or recommended through AI-powered workflows
This creates a new AI agent security challenge. Instead of attacking users directly, attackers can attempt to manipulate the information that an AI agent reads and uses when making recommendations or taking actions.
In this article, we explore 8 security risks of AI agents, including malicious tools, indirect prompt injection, poisoned software, fake reputation signals, malicious skills, and AI-enabled software supply-chain attacks.
AI Agents Are Becoming a New Malware Distribution Channel
Traditional malware campaigns often rely on phishing emails, malicious websites, fake downloads, or compromised software. AI agents introduce another possible route.
An AI agent can discover software, evaluate documentation, recommend tools, install packages, access repositories, and execute commands depending on its permissions. If the information it relies on has been manipulated, the agent may unknowingly direct a user toward malicious software.
The recent FakeGit campaign illustrates this concern. According to AI News, the campaign involved roughly 7,600 fake GitHub repositories, 6,600 fraudulent profiles, and more than 14 million downloads. More than 800 repositories reportedly impersonated AI skills and MCP servers and distributed malware such as SmartLoader and StealC.
The important issue is not necessarily that the AI model itself has been compromised. Instead, attackers can manipulate the AI software supply chain and the external information that agents use.
That distinction matters because AI agents increasingly act as intermediaries between people and the software ecosystem.
1. AgentBaiting Can Trick AI Assistants Into Recommending Malware
One of the most interesting risks is AgentBaiting.
Instead of convincing a human that a malicious repository is legitimate, attackers create content designed to look trustworthy to an AI assistant.
Fake repositories can contain:
- Professional-looking documentation
- Realistic project descriptions
- Fake contributor histories
- Artificial GitHub stars
- High download numbers
- Relevant keywords
- Familiar company or product names
The goal is to make malicious software appear relevant and trustworthy.
According to the reported FakeGit research, Gemini and ChatGPT independently recommended the same malicious Walmart-themed MCP repository in testing. The repository was not associated with Walmart, and Walmart’s systems were not reported as compromised. The malicious repositories were instead designed to appear legitimate and distribute malware.
This demonstrates why AI agent security cannot depend only on the model’s ability to understand language.
An agent may correctly understand a request such as “find a Walmart MCP connector” while still selecting a malicious result because the external trust signals have been manipulated.
2. Tool Poisoning Can Hide Malicious Instructions
Another major AI cybersecurity risk is tool poisoning.
AI agents frequently use tools through structured interfaces. One important example is the Model Context Protocol, or MCP, which allows AI applications to connect with external tools and data.
The problem is that tool descriptions are often presented to AI models as text.
An attacker could attempt to place hidden or misleading instructions inside a tool description. If an agent interprets those instructions as legitimate, the tool could potentially influence what the agent does next.
AI News referenced an earlier demonstration in which instructions embedded in a malicious calculator tool could manipulate another trusted email connector into copying outgoing messages to an attacker. The example was a demonstrated threat model rather than evidence of a confirmed real-world incident.
This is why organizations developing custom AI solutions should treat tool descriptions, connectors, and external instructions as potentially untrusted inputs.
Strong permission boundaries should exist between the AI model and sensitive business systems.
3. AI Agents Can Be Manipulated Through Indirect Prompt Injection
Prompt injection is not limited to messages that users directly send to an AI system.
With indirect prompt injection, malicious instructions can be hidden inside external content.
For example, an AI agent could visit:
- A webpage
- A GitHub repository
- A PDF
- An email
- A documentation page
- A software package
- An MCP tool description
That content could contain instructions specifically designed to influence the agent.
The agent may interpret the malicious text as part of the task it needs to perform.
This creates a fundamental challenge for autonomous AI security. An agent needs to understand external information while also recognizing that the information may be adversarial.
Security researcher Simon Willison has described a combination of three conditions as the “lethal trifecta”: access to valuable information, exposure to untrusted content, and the ability to send information externally. AI News cited this framework when discussing agent vulnerabilities.
The more permissions an agent has, the greater the potential consequences of successful manipulation.
4. Rug Pull Attacks Can Turn Trusted Tools Into Malware
Another risk is the software rug pull.
In this scenario, software initially behaves normally and builds a reputation. After users begin trusting and installing it, a later update introduces malicious functionality.
This is particularly relevant to AI agents because agents may automatically interact with tools and software packages.
AI News reported on a 2025 case involving a malicious connector that impersonated the Postmark email service. Earlier versions appeared harmless, while a later version reportedly introduced a hidden BCC recipient that copied emails to an attacker-controlled domain. The connector was not a Postmark product, and Postmark’s own service was not reported as compromised.
This illustrates why AI software security must extend beyond checking software at the moment it is installed.
Organizations also need to monitor:
- Version changes
- Package updates
- Dependencies
- New permissions
- Network activity
- Unexpected data transfers
Trust should not be permanent simply because an application passed an earlier security review.
5. External Dependencies Can Create Hidden Security Risks
AI agents increasingly depend on large ecosystems of packages, tools, repositories, APIs, and external websites.
This creates a broader AI software supply chain problem.
Even when an organization reviews the original source code, malicious behavior can potentially enter through a dependency or external resource that changes later.
AI News cited a 2025 security disclosure involving Cursor and a vulnerability called MCPoison, where attackers could modify previously approved project configurations and execute commands without renewed approval. The reported issue was subsequently addressed by Cursor.
This shows why reviewing the initial code is not always enough.
Security teams should also monitor the complete chain of dependencies used by an AI agent.
For businesses implementing AI, this makes AI integration security an important part of software architecture rather than an afterthought.
6. Opening an Untrusted Repository Can Create an Execution Risk
AI-powered coding environments introduce another layer of risk.
Developers increasingly use AI coding agents that can inspect repositories, execute commands, modify files, install packages, and interact with development environments.
If an unfamiliar repository contains malicious configuration instructions, simply opening or working with the project could create an attack path.
AI News reported security issues involving Claude Code that could allow repository-controlled configuration commands to execute and potentially expose API credentials through a manipulated server endpoint. Anthropic subsequently patched the reported vulnerabilities.
The lesson is important for AI coding security.
A repository should not automatically be considered safe simply because it contains source code rather than an executable application.
AI agents can transform information inside that repository into actions.
7. ClickFix-Style Attacks Can Make Users Execute Malware
Not every AI-related malware attack requires sophisticated prompt injection.
Attackers can also use familiar social-engineering techniques.
A malicious README or SKILL.md file could present a command as a required installation step. A user may copy and paste the command because an AI agent or repository makes the instruction appear legitimate.
This type of attack can combine malware distribution, social engineering, and AI automation.
AI News discussed the ClawHavoc campaign, where researchers identified malicious skills disguised as cryptocurrency and productivity tools within the OpenClaw ecosystem. The reported malicious skills targeted information such as browser credentials, API keys, SSH keys, cryptocurrency wallets, and Telegram sessions.
For organizations, this means employees should not automatically trust installation commands simply because they appear inside an AI-related project.
Security policies should clearly define which tools and packages AI agents are allowed to access.
8. AI Agents Could Automate Offensive Cybersecurity Operations
The most advanced concern is what happens when AI agents are connected to offensive security tools.
AI agents can already analyze information, execute commands, call tools, and coordinate multiple steps. When these capabilities are connected to penetration-testing or other security tools, attackers could potentially automate parts of a cyber operation.
AI News discussed Anthropic’s reporting on a campaign called GTG-1002, in which attackers reportedly connected penetration-testing tools to Claude Code through MCP. Anthropic said the model performed approximately 80% to 90% of tactical operations while human operators established objectives and made major strategic decisions. Anthropic attributed the activity to a state-sponsored group, although that attribution was not independently confirmed in the cited public threat-intelligence sources.
This does not mean that AI agents independently conduct every cyberattack.
Instead, it demonstrates why AI agent cybersecurity needs to consider how automation can change the speed and scale of existing attack techniques.
Why Fake Reputation Is a Growing AI Security Problem
A recurring theme across these attacks is manufactured trust.
Attackers can create fake stars, downloads, reviews, contributor histories, documentation, or other signals that make malicious software look legitimate.
AI agents may use these signals when searching for software.
That creates an unusual problem: a traditional user might inspect a project manually, but an AI assistant could process thousands of results and quickly select one based on relevance and apparent credibility.
The AI does not necessarily know whether those signals were artificially created.
As a result, popularity should not be treated as proof of security.
Organizations need stronger methods for verifying the origin and integrity of AI tools, packages, connectors, and skills.
How Businesses Can Reduce AI Agent Security Risks
Businesses adopting autonomous AI systems can reduce exposure by combining technical controls with clear governance.
Use Least-Privilege Access
AI agents should receive only the permissions required for their specific task.
An agent that summarizes documents does not necessarily need permission to send emails, modify databases, or execute arbitrary code.
Verify Tools and Software
Organizations should establish approved sources for AI skills, MCP servers, packages, and connectors.
Software provenance should be checked before an agent is allowed to use a new tool.
Monitor Agent Activity
Logging should capture important agent actions, including:
- Tools accessed
- Files opened
- Commands executed
- APIs called
- Data transferred
- Permission changes
- Authentication events
Monitoring can help security teams identify unusual behavior quickly.
Add Human Approval for Sensitive Actions
High-impact actions should require human confirmation.
Examples include:
- Sending sensitive information
- Executing privileged commands
- Installing unknown software
- Changing production systems
- Accessing financial systems
- Modifying security controls
Separate Trusted and Untrusted Content
AI agents should not automatically treat every webpage, repository, document, or tool description as trustworthy.
Businesses building AI development and machine learning solutions should incorporate trust boundaries directly into the architecture.
You can also explore professional AI and machine learning solutions for approaches to building AI systems with appropriate security, integration, and governance considerations.
What This Means for the Future of AI Agents
AI agents are becoming more useful because they can do more than generate text. They can search, reason, use tools, write code, interact with applications, and automate workflows.
That same capability creates a larger attack surface.
The emergence of AI agent malware does not mean that every AI agent is unsafe. It means that security models designed for traditional applications may not be sufficient for systems that can independently interpret information and take actions.
The FakeGit example is particularly important because it demonstrates a shift in the attack strategy. Instead of targeting only people, attackers can also attempt to influence the AI systems people rely on to discover and evaluate software.
This makes AI security a shared responsibility between AI developers, software vendors, cybersecurity teams, developers, and end users.
As AI agents gain more access to business data and digital infrastructure, organizations will need stronger authentication, permission controls, software provenance, monitoring, sandboxing, and human oversight.
The future of AI will not depend only on making agents smarter. It will also depend on making them harder to manipulate.
Conclusion
AI agents are becoming a new malware distribution channel because attackers can potentially exploit the trust, tools, software repositories, and external information that agents use.
The eight risks discussed here show how broad the challenge has become: AgentBaiting, tool poisoning, indirect prompt injection, rug pulls, compromised dependencies, malicious repositories, social engineering, and automated offensive operations.
For businesses, the key lesson is simple: an AI agent should not automatically trust the software, instructions, or information it encounters.
As autonomous AI becomes part of everyday business operations, AI agent security will need to become a core part of application security, software supply-chain security, and enterprise AI governance.
Frequently Asked Questions
What are AI agents?
AI agents are systems that can understand tasks, use tools, access data, and complete actions with limited human input.
How can AI agents spread malware?
Attackers can create fake repositories, tools, or AI skills that appear legitimate and may be recommended or used by AI agents.
What is AgentBaiting?
AgentBaiting is a technique that tricks AI assistants into recommending malicious software using fake trust signals.
What is prompt injection?
Prompt injection uses hidden or malicious instructions in content such as websites, files, or tool descriptions to influence an AI agent.
How can businesses secure AI agents?
Use limited permissions, trusted tools, monitoring, sandboxing, authentication, and human approval for sensitive actions.
Why is AI agent security important?
AI agents can access data, code, tools, and systems, creating new security risks if they are manipulated or compromised.